How to Remove Cookie Banners from Screenshots (Free and Growth Options)
Remove cookie consent banners from automated screenshots: blockAds on every plan, hideSelectors and AI removal on Growth. Exact request fields, known limits and a reproducible before/after.
Cookie consent banners sit on top of the content you are trying to capture. This guide shows the four ways Screenshotly can keep them out of an automated screenshot, which plan each one needs, and where each one stops working.
All requests below go to POST https://screenshotly.app/api/screenshot with your key in the x-api-key header (a Authorization: Bearer header also works). The full parameter list is in the screenshot API reference.
The short answer
| Option | Request field | Plan | How it works | Best for |
|---|---|---|---|---|
| Built-in banner filtering | blockAds: true |
All plans, including Free | Blocks a fixed list of consent, ad, analytics and chat domains, then hides a fixed list of CSS selectors | Common consent tools and conventional class names |
| Your own selectors | hideSelectors: [".your-banner"] |
Growth+ | Adds display: none !important for each selector you list |
Sites you know, including your own |
| AI removal | aiRemoval: { enabled: true, types: ["cookie-banner"] } |
Growth+ | A hosted language model classifies candidate elements and hides the matches | Many third-party sites with unpredictable markup |
| A real consent state | cookies: [...] (Basic+) or javascript (Growth+) |
Basic+ / Growth+ | Sets the site's consent cookie, or clicks the consent button | Captures that must show the page after a choice |
Start with blockAds. Add a selector when you know the markup, and turn on AI removal only for the sites the first two miss.
Option 1: blockAds (every plan)
curl -X POST https://screenshotly.app/api/screenshot \
  -H "x-api-key: $SCREENSHOTLY_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{"url":"https://example.com","blockAds":true,"format":"png"}' \
  --output clean.png
blockAds does two deterministic things. It is defined in the product's ad-blocker module, so the behaviour below is exact rather than approximate:
- Request blocking. Requests to a fixed domain list are aborted before they load. For consent tools that list includes
cdn.cookielaw.org,cookiebot.com,trustarc.comandconsensu.org. If the banner script never loads, the banner never renders. The same list also covers ad networks, analytics and chat vendors (for exampledoubleclick.net,googletagmanager.com,hotjar.com,intercom.ioandhubspot.com). - Selector hiding. After the page's DOM is ready, a stylesheet hides consent elements whose class or id contains
cookie-consent,cookie-banner,cookie-notice,cookie-popup,consent-bannerorconsent-popup. It also hides ids that containgdpr, plus.cc-banner,.cc-window,.cc-revoke,#onetrust-banner-sdk,#onetrust-consent-sdk,.cky-consent-containerand.cky-notice. Because it is a stylesheet, it also hides matching elements that appear later.
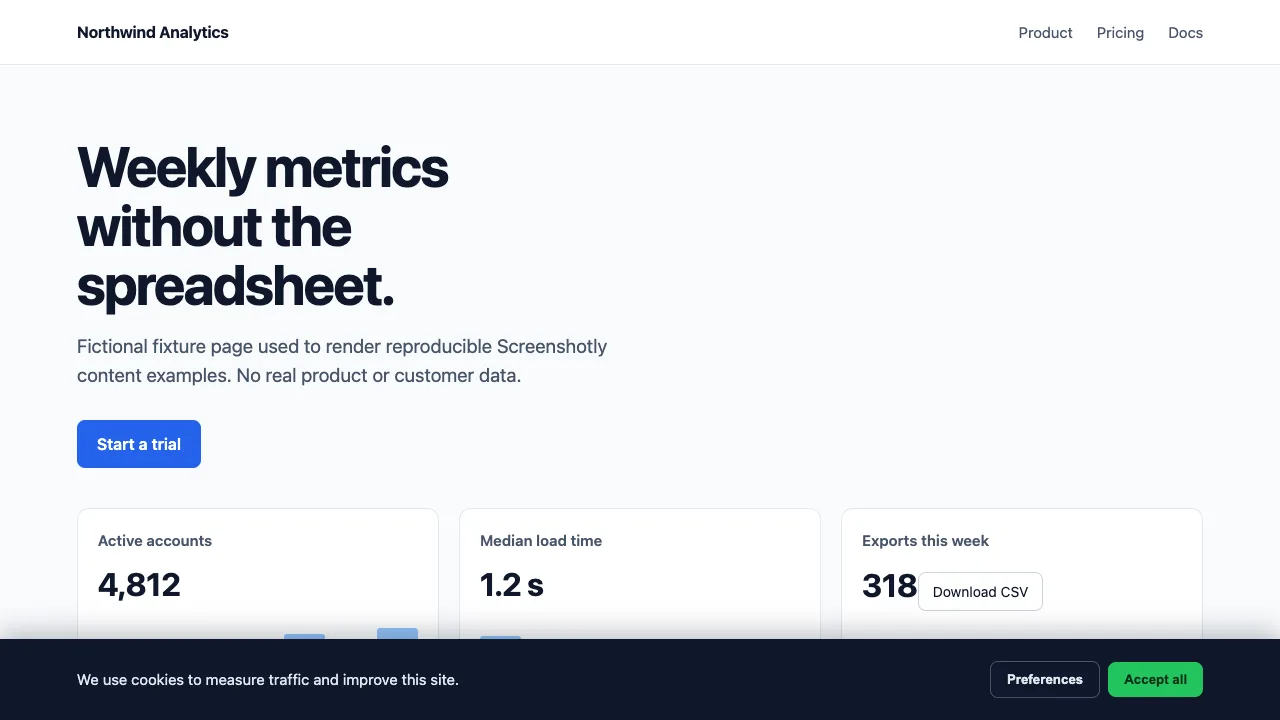
#onetrust-banner-sdk container, rendered without blockAds.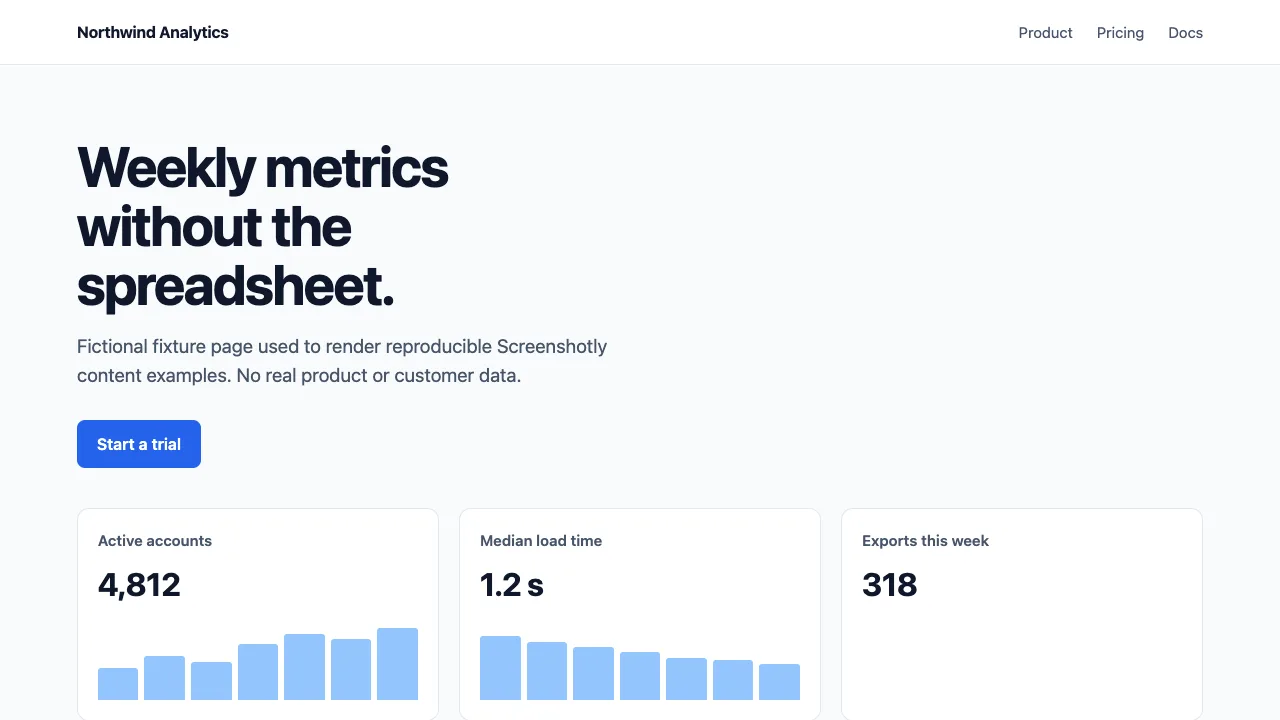
blockAds: true. The banner is hidden, but so is the Download CSV button (see the limits below).These images come from a fictional local fixture page, not a customer site. They were rendered with the same stylesheet and domain list that blockAds ships with, using scripts/content-fixtures/render-feature-evidence.ts in the Screenshotly repository. They are not production API captures.
Where blockAds stops working
- Custom banner markup. A banner such as
<div class="privacy-drawer">matches none of the built-in selectors and stays visible. In the fixture render below,blockAdswas on and the banner still shows. - Over-matching. The ad-hiding rules include substring selectors such as
[class*="ad-"]. Those also match ordinary class names that happen to containad-, such asdownload-button,thread-listorupload-btn. In the fixture, the Download CSV button disappeared for exactly this reason. Compare a capture with and withoutblockAdsbefore you rely on it for a page you care about. - Blocked first-party pages. If the page you capture is itself hosted on a listed domain (for example a page on
hubspot.com), the page request is blocked too. LeaveblockAdsoff for those targets. - Side effects of blocking the consent tool. Some sites hold back embeds or other content until their consent tool loads. With the tool blocked, that content may not appear.
- Scroll locks and backdrops. If the site locks scrolling or dims the page while the banner is open, hiding the banner element does not undo that.
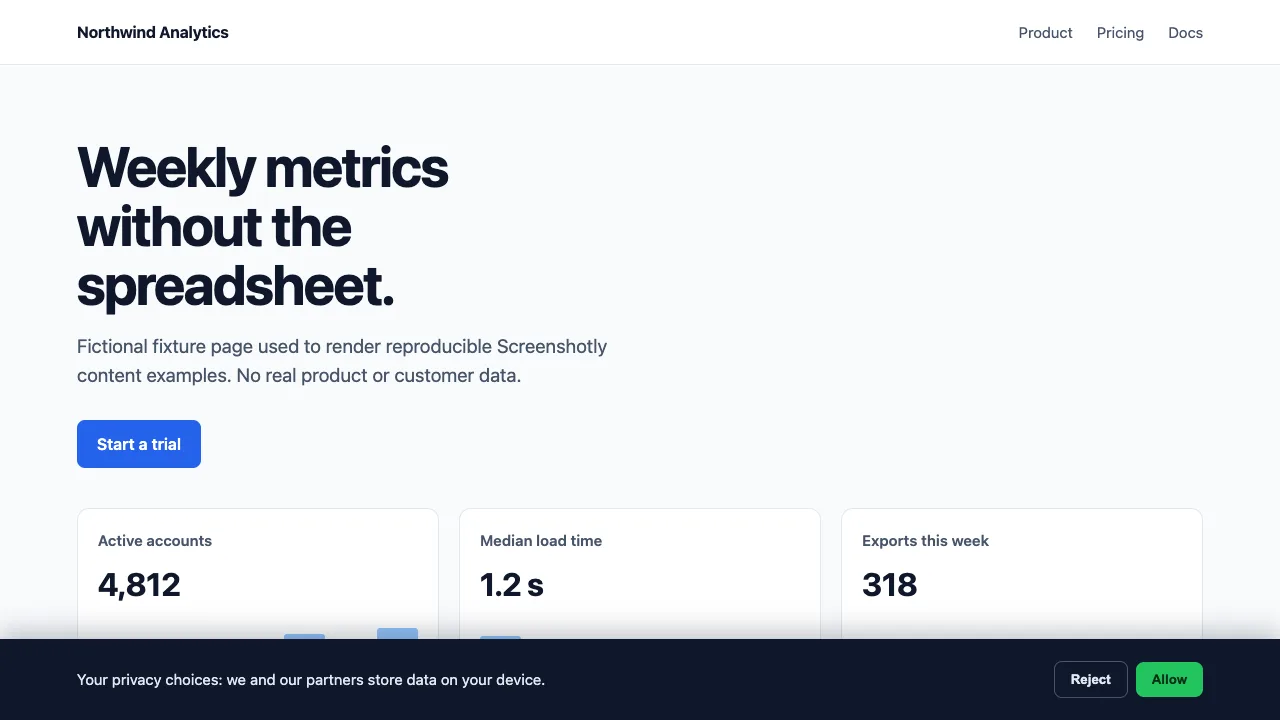
.privacy-drawer banner is not covered by the built-in selectors, so blockAds alone leaves it in place.Option 2: hideSelectors (Growth+)
When you know the banner's markup, list it. Each selector gets display: none !important; visibility: hidden !important;. You can send up to 100 selectors.
curl -X POST https://screenshotly.app/api/screenshot \
  -H "x-api-key: $SCREENSHOTLY_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{"url":"https://example.com","blockAds":true,"hideSelectors":[".privacy-drawer"],"format":"png"}' \
  --output clean.png
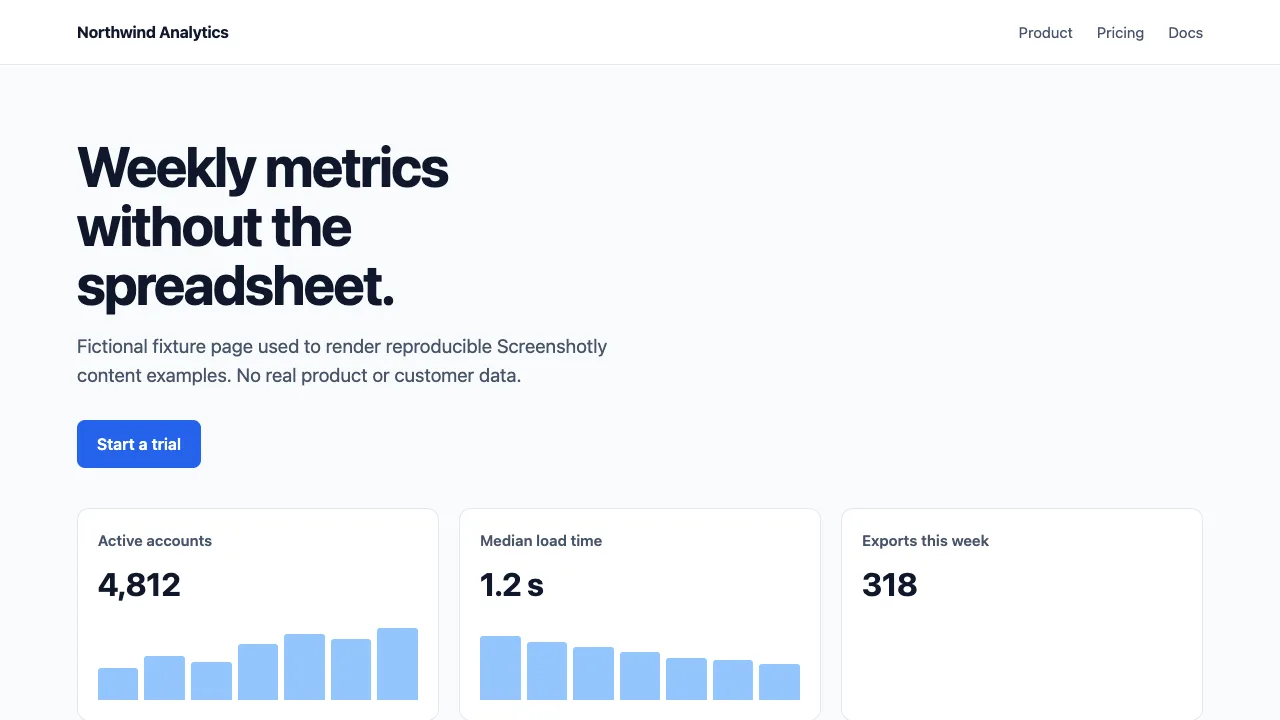
hideSelectors: [".privacy-drawer"] added. The banner is gone. The Download CSV button is still hidden because blockAds is still on.Selectors are the most predictable option for your own product or a fixed list of pages. They break when the site renames its classes, so pin them in one place and review failed captures.
Option 3: AI removal for cookie banners (Growth+)
For third-party sites you do not control, ask the AI pass to look for consent banners only:
curl -X POST https://screenshotly.app/api/screenshot \
  -H "x-api-key: $SCREENSHOTLY_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{"url":"https://example.com","blockAds":true,"aiRemoval":{"enabled":true,"types":["cookie-banner"],"confidence":0.8},"format":"png"}' \
  --output clean.png
How it decides, in brief:
- After
blockAds, any custom JavaScript,delayandhideSelectorshave run, the browser collects up to 300 candidate elements. An element is a candidate if it is fixed or sticky, or if its id, class, role or aria-label mentions words like cookie, consent, modal or overlay. - A hosted language model labels the candidates using that metadata (tag, id, class, role, aria-label and CSS position). It does not see pixels or the page's body text.
- Matches labelled
cookie-bannerwith a confidence of at leastconfidence(default0.8, range 0–1) are hidden withdisplay: none.
What to expect:
- It only hides what it is asked about.
types: ["cookie-banner"]leaves chat widgets and newsletter modals alone. If you omittypesor send an empty list, all five types are considered:cookie-banner,newsletter,chat-widget,social-overlayandad. - It can still miss or mislabel elements. Markup with no meaningful names gives the model little to work with, and banners inside iframes or shadow DOM are not inspected.
- It is all-or-nothing on errors. If the model call fails, the request fails with HTTP 500 instead of returning an uncleaned image. Failed captures do not use quota.
- Without the Growth plan the API answers
403with{"error":"Plan upgrade required","minimumPlan":"growth"}.
We have not published a before/after for AI removal because it depends on a live model call. To check it on your own pages, capture the same URL with and without aiRemoval and compare. The AI element removal guide covers tuning and debugging in more depth.
Option 4: capture the page after a real consent choice
Hiding a banner is different from answering it. If the screenshot should show what a visitor sees after accepting or rejecting cookies (for example, embedded media that only loads after consent), set the consent state instead.
On sites you own (Basic+): send the cookie your consent tool writes when a visitor makes a choice. The name and value below are placeholders; use the ones your own site sets. The cookie domain must be the target host or one of its parent domains, otherwise the API rejects the request with HTTP 400.
curl -X POST https://screenshotly.app/api/screenshot \
  -H "x-api-key: $SCREENSHOTLY_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{"url":"https://www.example.com/pricing","cookies":[{"name":"site_consent","value":"rejected","domain":"www.example.com"}],"format":"png"}' \
  --output after-choice.png
Click the button (Growth+): the javascript field runs after the DOM is ready and before the capture (up to 5,000 characters). If the script throws, the capture continues without it.
curl -X POST https://screenshotly.app/api/screenshot \
  -H "x-api-key: $SCREENSHOTLY_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{"url":"https://www.example.com","javascript":"document.querySelector(\"[data-consent=reject]\")?.click()","delay":1000,"format":"png"}' \
  --output after-click.png
Only automate a consent choice on sites where you are entitled to make it, typically your own. These techniques change how the capture browser behaves. They are not legal advice and do not change anyone's consent obligations.
Which option should you use?
- Screenshots of your own product or docs:
blockAds, thenhideSelectorsfor anything left. Use a consent cookie if you need the post-choice state. - A fixed list of third-party pages:
blockAdsplus a shorthideSelectorslist per site. Keep the list under version control. - Many or unknown third-party sites:
blockAdsplusaiRemovalwithtypes: ["cookie-banner"]. Review a sample of the outputs regularly. - Visual regression baselines: prefer the deterministic options (
blockAds,hideSelectors). An AI decision can differ between runs, and that shows up as a diff.
The cookie banner removal feature page summarises these options in one place. Plan limits are on the pricing page.
About the Author

Asad Ali
CTO at ZTABS and the developer behind Screenshotly. Writes about screenshot automation, API design, and building reliable SaaS backends with Next.js, Node.js, and TypeScript.
Credentials: CTO at ZTABS, full-stack developer, builder and maintainer of Screenshotly and its official JavaScript and Python clients
Frequently Asked Questions
Can I remove cookie banners on the Free plan?
Yes. Set blockAds: true. It is available on every plan, including Free. It aborts requests to a fixed list of consent, ad, analytics and chat domains and injects CSS that hides a fixed list of common consent-banner selectors. It does not use AI.
When do I need AI removal instead of blockAds?
When the banner uses its own markup that matches none of the built-in selectors and you cannot list a selector for it yourself, for example when you capture many third-party sites. AI removal (aiRemoval with types ['cookie-banner']) needs the Growth plan or higher.
Does hiding the banner accept or reject cookies?
No. blockAds, hideSelectors and aiRemoval only hide elements or block requests in the capture browser. They do not click a button or record a consent choice. If you need the page as it looks after a choice, set your own consent cookie (Basic+) or click the button with custom JavaScript (Growth+).
What happens if I send aiRemoval on a Free or Basic key?
The API returns HTTP 403 with error 'Plan upgrade required' and minimumPlan 'growth'. Nothing is captured and no quota is used.
Ready to capture your first screenshot?
Get started with 100 free screenshots. No credit card required.